A certification checkout Stripe couldn't build on its own.
Senior Select Seal sells a professional certification with a pricing shape Stripe doesn't natively support: per-license volume discounts stacked on top of multi-year renewal prepay, all as one-time charges. I designed and built the system that makes it work — and when I was told it was already live, I checked, and it wasn't.
The pricing problem
What the business needed to sell, in plain terms
Every certification purchase covers one year of access. At checkout, the buyer can also prepay 0, 1, 3, or 5 years of renewal in advance, locking in a discounted renewal rate permanently — and that per-license price then gets a further volume discount at 5, 10, and 20 licenses.
That's 4 renewal tiers × 4 volume tiers of real, distinct prices, computed from quantity and choice at the moment of purchase. I confirmed directly against Stripe's API that tiered pricing like this isn't available on one-time charges at all — it's subscription-only. The fix was to stop asking Stripe to store the pricing and have the backend compute it fresh on every checkout instead.
What I built
A Cloudflare Worker as the checkout's actual brain
Dynamic pricing, not static Prices
The Worker computes the exact per-license amount server-side from the renewal choice and quantity, then creates the Stripe Checkout Session with that price attached directly — no pre-built Price object for every combination, no coupon codes to keep in sync by hand.
Payment ≠ access
A successful charge only creates a pending order. Nobody gets course access — not even a single-license buyer — until they open a signed link, read the real terms of their specific order (price, renewal rate, expiration date, the works), type their legal name, and check an explicit "I agree." Only then does the Worker grant Kajabi access.
A free, legally sound e-signature
Rather than pay for DocuSign or a similar service, I built the capture mechanism myself: typed name, explicit checkbox, timestamp, submitter IP, and the exact agreement text shown — stored as an audit record. That combination satisfies the US ESIGN Act / UETA for an agreement this straightforward.
Shipping on a claim, not trusting it
"It's deployed" turned out to mean three different things were silently broken
Instead of accepting that the checkout was live once told so, I ran an actual end-to-end purchase and checked what happened downstream. Nothing had: zero orders had ever been recorded.
- No webhook existed. Stripe's own dashboard showed zero webhook destinations configured for this flow —
checkout.session.completedhad never once reached the backend, for any purchase, ever. - Two required secrets were missing from the Worker's config entirely, so even a wired-up webhook would have failed signature verification and the Kajabi grant both.
- The post-payment redirect pointed at a URL with no route attached to it — a successful payment would have sent the buyer to a dead page, and the signature-request email would have shipped a dead link.
All three got fixed before anything was called "working" again — including rewriting the base URL logic to derive itself from the actual incoming request, so it's correct regardless of which domain ends up serving it.
Course delivery, wired correctly the second time
Kajabi's real API, not the shortcut that looked like it would work
Course access runs through Kajabi tag-triggered automations: one tag grants the offer, a second triggers the "please sign" email — using Kajabi's own transactional email, at no extra cost, instead of adding a third-party email provider. Getting there meant replacing a naive static API key with Kajabi's actual OAuth2 client-credentials exchange once I confirmed the key Kajabi issues is a client ID/secret pair, not a bearer token the old approach assumed.
The result
What a buyer actually sees
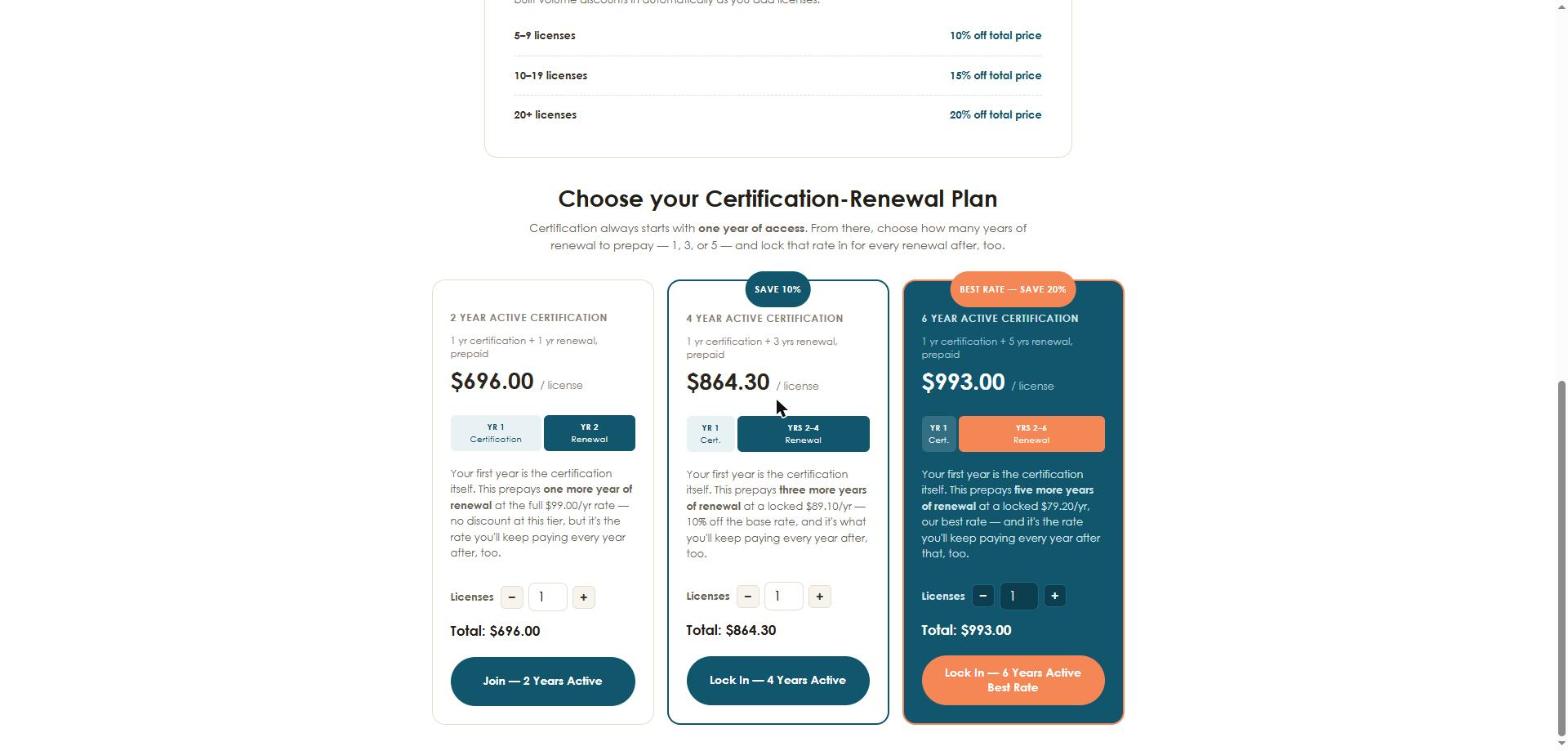
The live pricing tiers, computed by the Worker in real time instead of stored as static Stripe Prices.
Where it stands
The build is live on Senior Select's live Stripe account — live Products, a live webhook, and a restricted live API key scoped to exactly the five permissions the Worker needs and nothing more. A full real-money purchase has been run end to end: checkout, the signed agreement, and the Kajabi access grant all completed successfully in production.